Outsource your network management
We manage your firewalls, switching, Wi-Fi, and SD-WAN as one integrated environment. Multi-vendor, monitored 24/7, with security at its core.
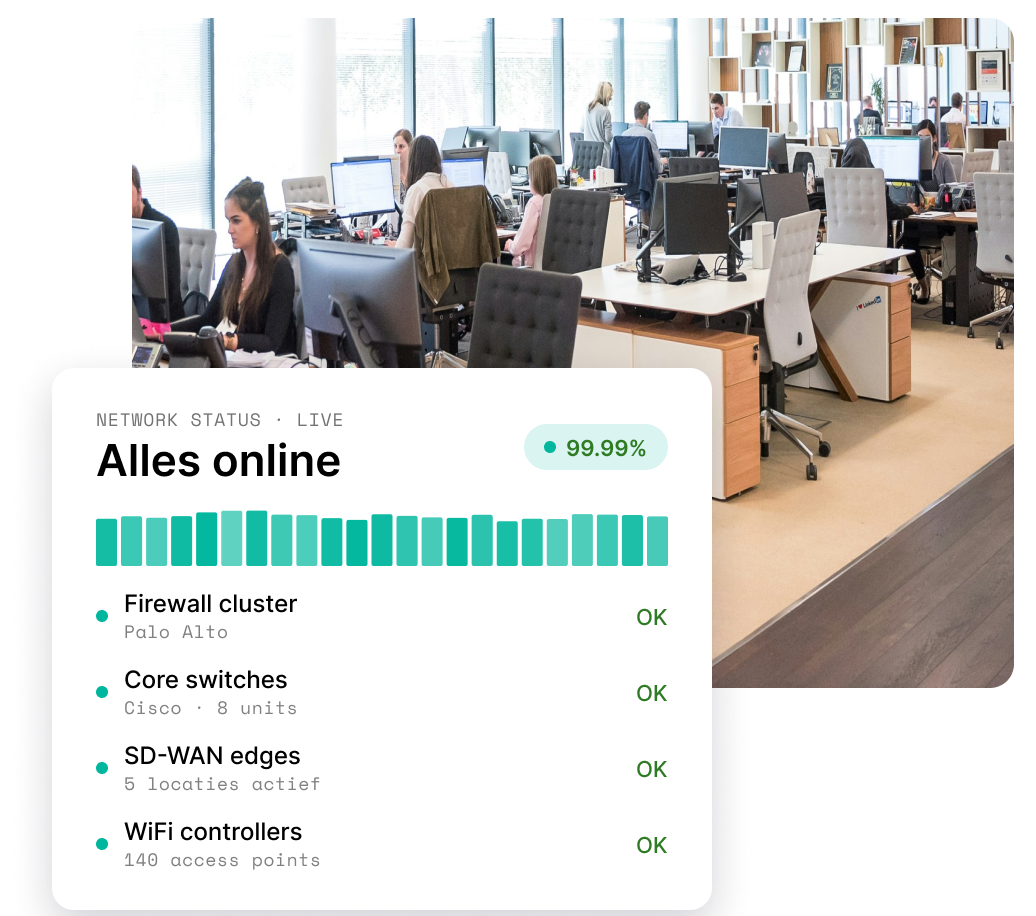
A growing business needs a network that grows with it.
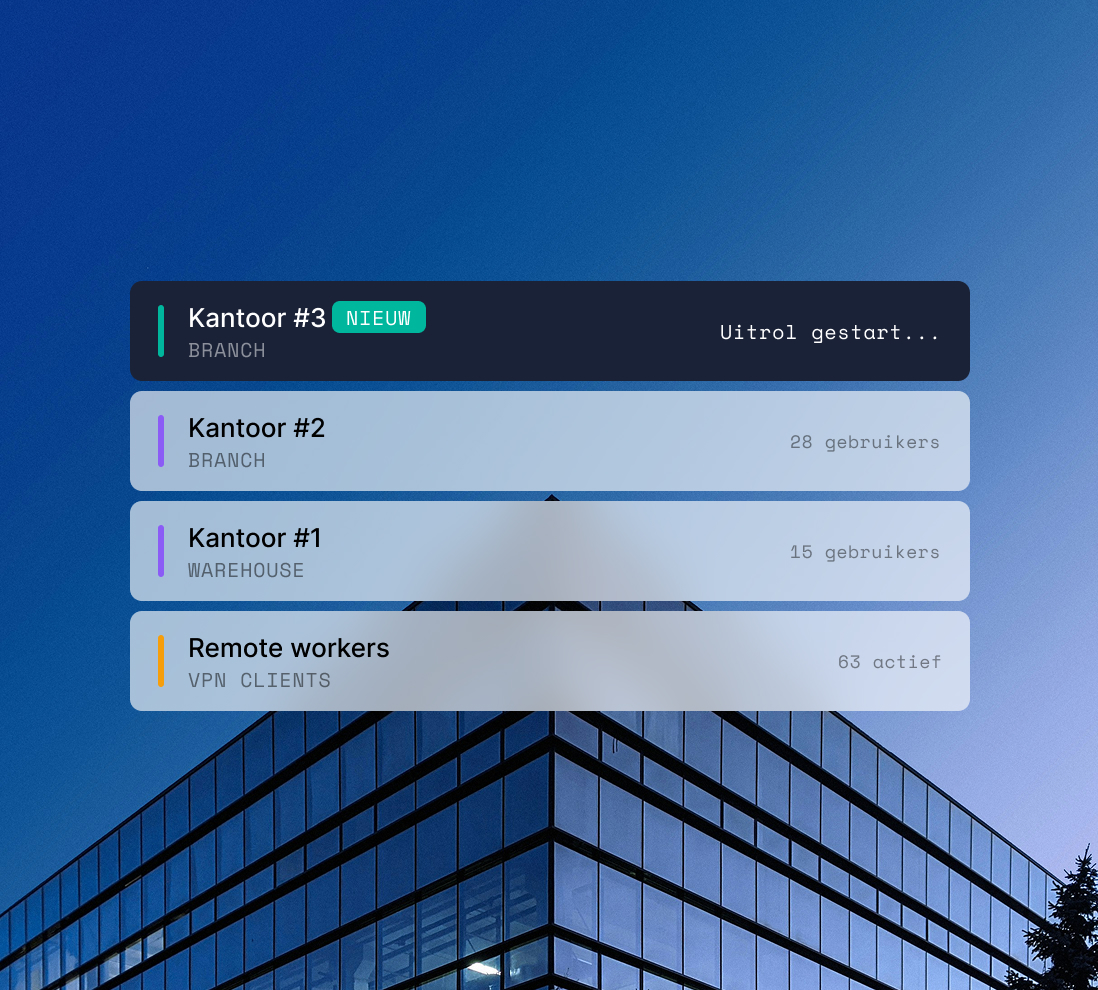
Locations, cloud connections, VPNs, firewalls, switches, Wi-Fi, and SD-WAN. What some see as “IT,” we see as business-critical infrastructure. We create structure through clear documentation, segmentation, and a scalable management model.
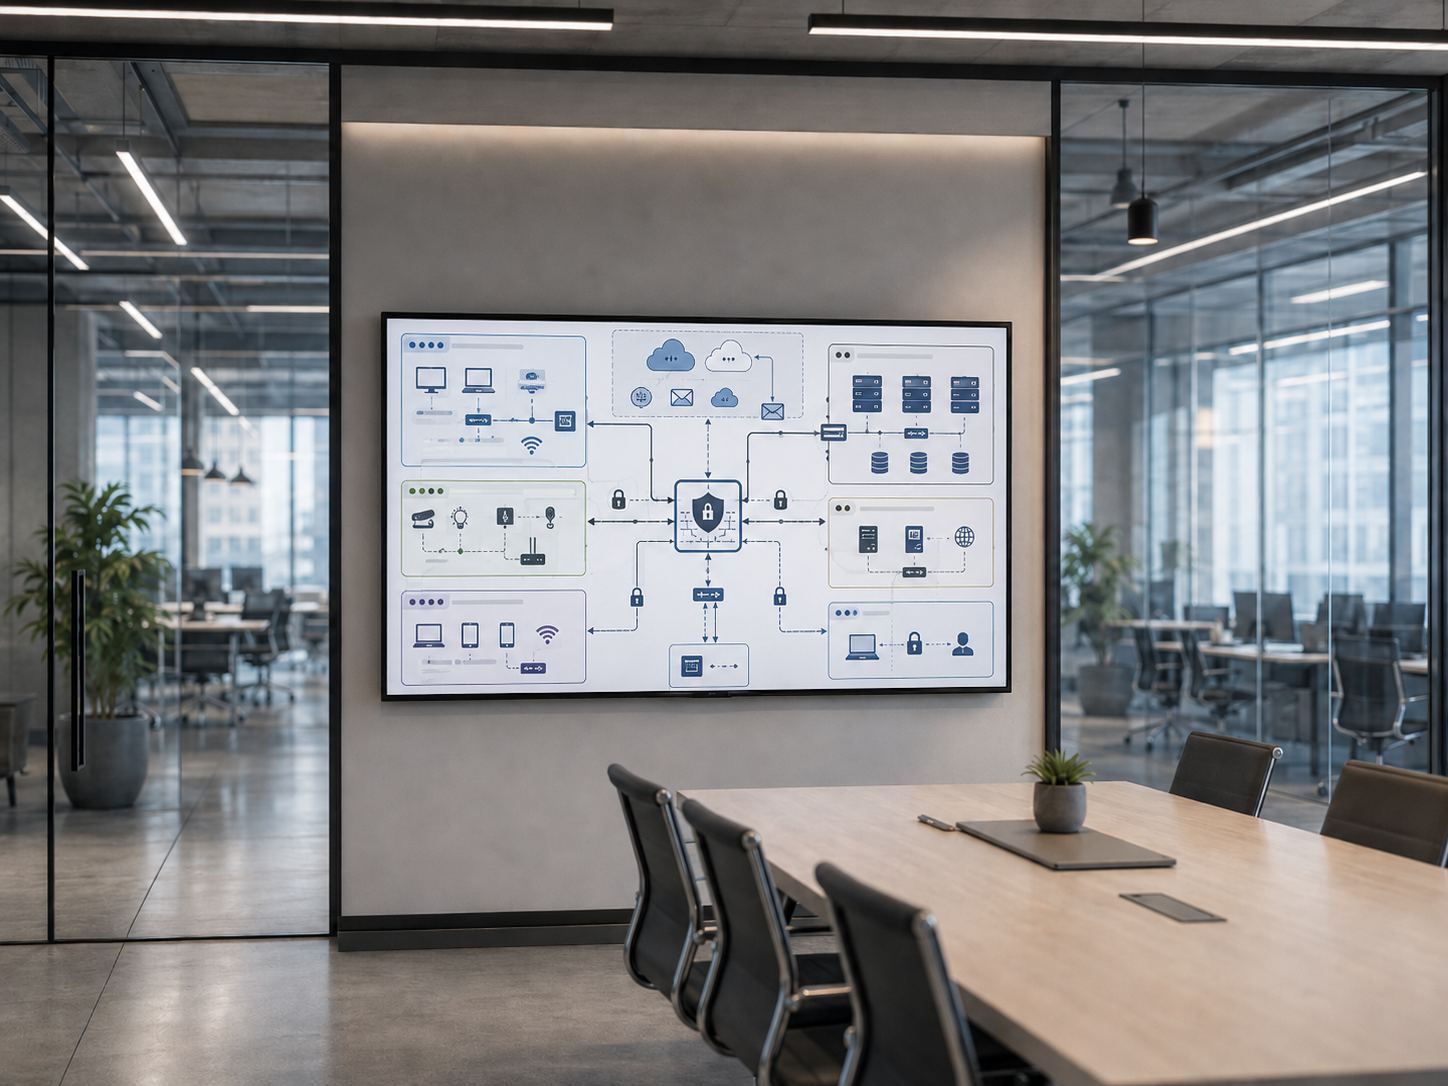
How we secure your network
Modern network management uses a layered architecture in which segmentation, identity, detection, and secure access work together to reduce the attack surface. We configure and manage all four layers as one integrated environment.
We divide the network into zones based on function and risk: office, production, guest, IoT, OT, servers, and management. Traffic between zones passes explicitly through the firewall under zone-specific policies. For sensitive environments, we use microsegmentation, giving each server or application its own security zone. A compromised device in one zone therefore cannot simply move laterally through the rest of the network.
No implicit trust based on location or IP address. Every connection is verified using identity, device state, and context. For remote access, we replace traditional VPNs with Zero Trust Network Access (ZTNA): users can access only the specific applications they need, not the entire network. Identity checks run through Entra ID with MFA and Conditional Access.
Next-generation firewalls with IDS/IPS detect known exploits, malware signatures, and anomalous traffic in real time. Threat intelligence feeds are updated continuously. Suspicious traffic is blocked automatically or placed in quarantine. Logs and alerts flow into our Security Operations Center (SOC), where security analysts monitor 24/7 and respond immediately to incidents.
SD-WAN provides intelligent traffic management between locations and the cloud, with automatic failover, application-aware routing, and lower costs than traditional MPLS. For organizations ready to go further, we integrate SD-WAN with cloud-delivered security in a SASE architecture: firewall, secure web gateway, ZTNA, and CASB are delivered from the cloud, close to where the user works. One consistent policy, whether someone is in the office, at home, or on the road.
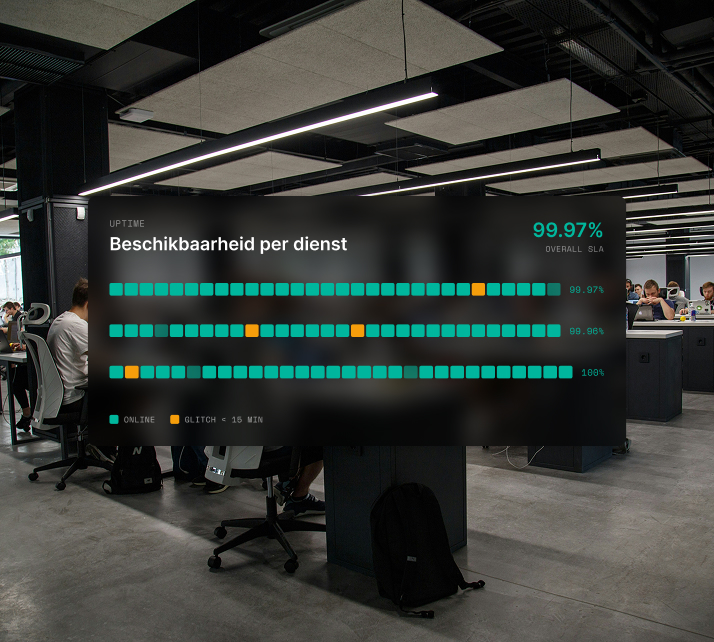
Uptime should never be left to chance
Your organization depends on connectivity. Downtime is not an option. That is why we build and manage networks designed for continuity, not best effort.
Built on proven technology.
Learn how our carefully chosen collaborations support your organization with reliable and scalable managed IT services.
Trusted by IT leaders in the Netherlands
Your IT and security partner for Dutch organizations for over 25 years.
Technology is powerful. Integration is critical.
We work with leading technology partners, but technology alone won't protect you. The right configuration, monitoring, and governance make all the difference.





Broad coverage with centralized expertise
You get a single point of contact, backed by the strength of a regional presence and specialized hubs across the country. This allows you to benefit from local engagement and shared expertise.

FAQ
Frequently asked questions about outsourcing network management
These are the questions organizations often ask us. Do you have another question?
Can't find your question?
No problem. Feel free to let us know what questions you have!
Costs depend on the size and complexity of your network: the number of locations, firewalls, users, and the required SLA. During an intake, we assess your environment and provide a transparent proposal.
No. We manage multi-vendor environments with Palo Alto, Fortinet, WatchGuard, and other enterprise solutions. Your existing investment remains usable. If replacement makes sense, we will recommend it explicitly and explain why.
A managed firewall means that we manage the complete lifecycle: configuration, policy updates, firmware patches, logging, monitoring, and incident response. You receive monthly reports on blocked threats, performance, and changes.
We start with a thorough assessment of the current topology, configurations, SLAs, and contracts. We then create a transition plan with quick wins and a phased handover.
Ready to outsource network management? Start with a conversation.


