Low-hanging fruit for hackers? Abandoned accounts and accumulated permissions from former employees that were never cleaned up. Permission sprawl and identity chaos pose a growing risk, and with stricter audits (ISO 27001, DORA, NIS2) on the horizon, a solution is essential.
We explain what identity lifecycle management is, why it is essential for large organizations under high compliance pressure, and how to implement it practically. We focus on environments with 1250+ users working with both Microsoft cloud and on-premises systems. We also discuss the result: control over all user and machine identities from onboarding to offboarding. In short, you will know what it delivers for your organization and why you need to act now.
What is identity lifecycle management?
Identity Lifecycle Management (ILM) is the structured management of digital identities (accounts) throughout their entire lifecycle within the organization. This covers every stage of an identity, from creation during onboarding to adjustments following role changes and deletion upon departure. The goal is to ensure that the right people (and systems) have the right access at the right time, and only for as long as necessary. As such, Identity Lifecycle Management (ILM) forms the foundation of Identity Governance.
Importantly, ILM is not just about user accounts, but also machine identities (such as service accounts, API keys, and certificates). Modern standards like ISO 27001:2022 require that the full lifecycle of identities be managed in a broad sense, for both humans and non-humans. This means that a server account or script user ID must be uniquely registered, authorized, and eventually cleaned up just like an employee account. Identity lifecycle management therefore extends to all entities that have access to systems in your IT environment.
Why is Identity Lifecycle Management important in 2025?
The need for ILM has never been greater. First, many large organizations struggle with permission sprawl: over time, users accumulate more privileges than strictly necessary, also known as privilege creep. Without lifecycle management, orphaned accounts (abandoned accounts belonging to former employees) and unnecessarily accumulated access rights that are never revoked begin to emerge. This dramatically increases the risk of misuse. The 2025 Verizon Data Breach Investigations Report revealed that 22% of all security breaches began with compromised credentials, and no less than 88% of attacks on web applications involved stolen credentials. A threat actor who uncovers an abandoned account or excess privileges has struck gold.
In addition, compliance and audit pressure has intensified significantly. New legislation such as the European NIS2 Directive mandates stricter, sector-wide measures for access and identity management. In the financial sector, the Digital Operational Resilience Act (DORA) requires financial institutions to manage user privileges in real time and conduct regular access reviews to prevent privilege creep. The Dutch NCSC emphasizes in their core principles, among other things: “Manage access: only grant employees access to the data and services necessary to perform their work.”. In other words, least privilege must be demonstrably enforced. This is only possible with rigorous identity lifecycle management.
At the same time, the costs and fallout of identity-related incidents are mounting. According to RSA’s ID IQ Report 2026, 69% of organizations have experienced an identity-related security incident over the past three years—a significant increase compared to the previous year.
The identity lifecycle management phases (Joiner–Mover–Leaver)
Identity lifecycle management is often divided into three main phases, also known as the Joiner-Mover-Leaver (JML) framework. These phases outline the lifecycle of a user identity within the organization:
- Joiner – when a new employee joins or an external contractor comes on board. A digital identity (account) must be created for this individual and provisioned with the correct baseline access rights (birthrights). For example: a new account in Microsoft Entra ID (Azure AD) with standard permissions for email, HR systems, and any role-based access required for the position. Ideally, this happens automatically as soon as HR logs a new hire, enabling the new user to get started securely right from day one.
- Mover – when an existing user changes roles, departments, or locations within the organization. This requires adjusting their access rights: permissions that are no longer needed must be revoked, and new permissions for the new role must be assigned. For example: an employee moves from Sales to Finance; access to Sales systems must be revoked, and access to Finance applications granted. A solid JML process executes this promptly so the user isn't left with too many or too few permissions. Automated detection of such changes (e.g., via HR updates or AD group changes) along with corresponding workflows eliminates a lot of manual work here. Human error represents the greatest risk.
- Leaver – when a user leaves the organization or no longer requires access. This is the critical offboarding phase: all access rights must be terminated on the departure date, and accounts deactivated or deleted. If necessary, orphaned accounts must be archived for future audits or investigations. An effective leaver process ensures no old accounts are accidentally left lingering. This includes immediately revoking network access, VPN, SaaS accounts, and physical access badges on the day of departure.
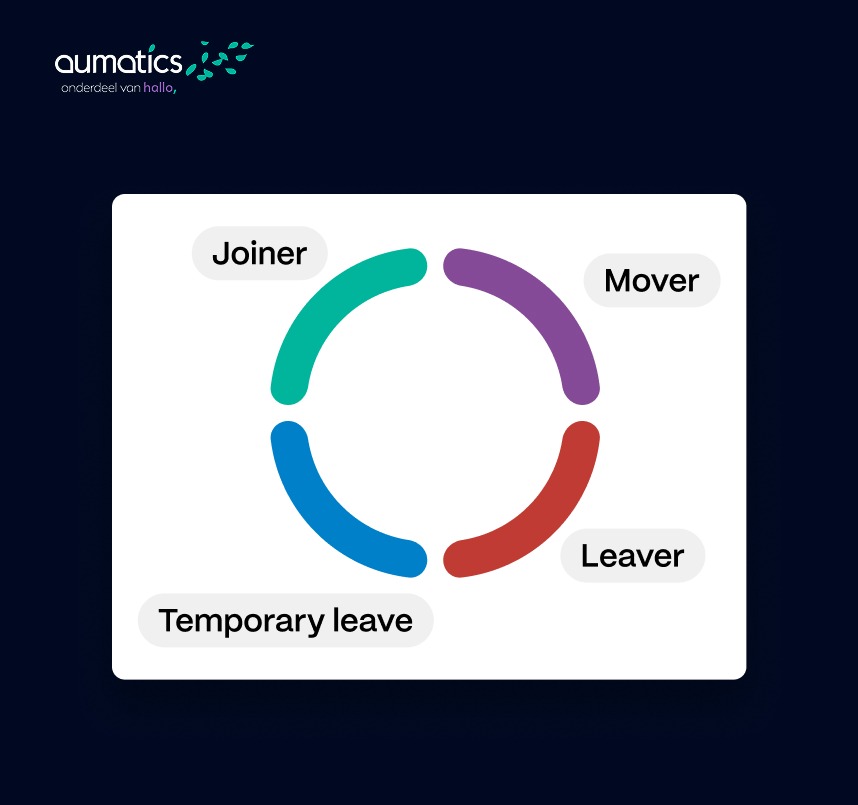
Together, these stages make up the user identity lifecycle management cycle. By implementing a standardized process for every joiner, mover, and leaver, you maintain complete control. What's more, you establish a logical audit trail: you can demonstrate when an account was created, modified, and deactivated, and who authorized it. Furthermore, this JML framework applies not only to internal staff, but also to external partners and guests who require temporary access.
Automated identity lifecycle management – automation as the key
In small organizations, identity management can still be handled with manual work and checklists. But in medium and large organizations, automation is indispensable to keep identities correct at scale. Automated identity lifecycle management means that as many steps as possible in the joiner-mover-leaver process are automated according to predefined workflows and policies. This has several advantages:
- Consistency & Speed: When someone joins or changes roles, accounts and permissions are instantly and accurately created or adjusted based on policy, eliminating delays and human error.
- No Overlooked Offboarding: Automation prevents accounts from lingering after an employee departs. As soon as HR enters a termination, the IAM system can automatically lock all linked accounts and stage them for deletion.
- Reduced Permission Sprawl: By predefining birthright access packages and roles (RBAC/ABAC) and enforcing SoD policies, users automatically receive only the minimum necessary permissions (least privilege).
- Audit-Ready Reporting: Automated ILM logs everything: who gained or lost which access, when it happened, and based on what request or event. This provides a complete audit trail for every "identity change."
In short, automated identity lifecycle management makes identity management more efficient, more secure, and auditable. Naturally, this cannot be achieved with a simple spreadsheet and a few partial API integrations. It requires dedicated tools and software.
Identity lifecycle management tools & solutions
Technology is an enabler for ILM. There are various identity lifecycle management tools and solutions on the market, ranging from built-in platform features to full-fledged stand-alone Identity Governance & Administration (IGA) suites. Here, we discuss two categories that are often relevant for Microsoft-oriented organizations: Microsoft Entra ID Governance and full-scale IGA solutions (such as RSA Governance & Lifecycle). Both can serve as an identity lifecycle management solution, but there are significant differences in scope and capabilities.
Microsoft Entra ID Governance
Microsoft Entra ID Governance is Microsoft’s built-in solution for identity governance within the Entra (formerly Azure AD) platform. It provides policy-based, largely automated capabilities to ensure the right people have the right access to the right resources, and only for as long as needed. Key capabilities include Lifecycle Workflows (JML workflow automation), Access Reviews (periodic recertification of access rights), Entitlement Management (access packages and self-service requests), and Privileged Identity Management (PIM) for administrative accounts.
Full-scale IGA solution (e.g., RSA Governance & Lifecycle)
For organizations looking beyond the Microsoft ecosystem and seeking full control over all identities in hybrid environments, a dedicated Identity Governance & Administration (IGA) solution is recommended. An example is RSA Governance & Lifecycle, a market-leading platform that delivers comprehensive governance, provisioning, and compliance functionality both on-premises and in the cloud. While Entra ID Governance focuses on Azure AD, RSA G&L acts as an overarching layer across all your systems and applications—from Microsoft to third-party platforms. This is particularly valuable when dealing with legacy provisioning, complex SoD requirements, and rigorous audit standards.
Our RSA expert explains when and why an IGA solution comes in handy:
User vs machine identity lifecycle management
Identity management has long focused on people, but machine identity lifecycle management is just as important. Machine identities, such as application accounts, service accounts, API tokens, RPA accounts, IoT identities, and certificates, also have a lifecycle: creation, usage, modification, and deletion.
In practice, machine accounts are often forgotten. They don't have an HR exit, persist after migrations, and thus become orphaned credentials with high privileges. Attackers love to exploit this because machine accounts are monitored less frequently and often have broad permissions. Identity lifecycle management must therefore encompass both human and non-human identities.
Getting started with Identity Lifecycle Management
Wondering how your organization can elevate identity lifecycle management? As a security-first MSP and RSA Gold Partner, Aumatics is here to help. Schedule an initial 30–45 minute consultation with our identity specialists today.