Managed EDR that detects and stops endpoint attacks
Our analysts monitor your laptops, servers, and workstations 24/7. Suspicious behavior is stopped immediately, before damage occurs.
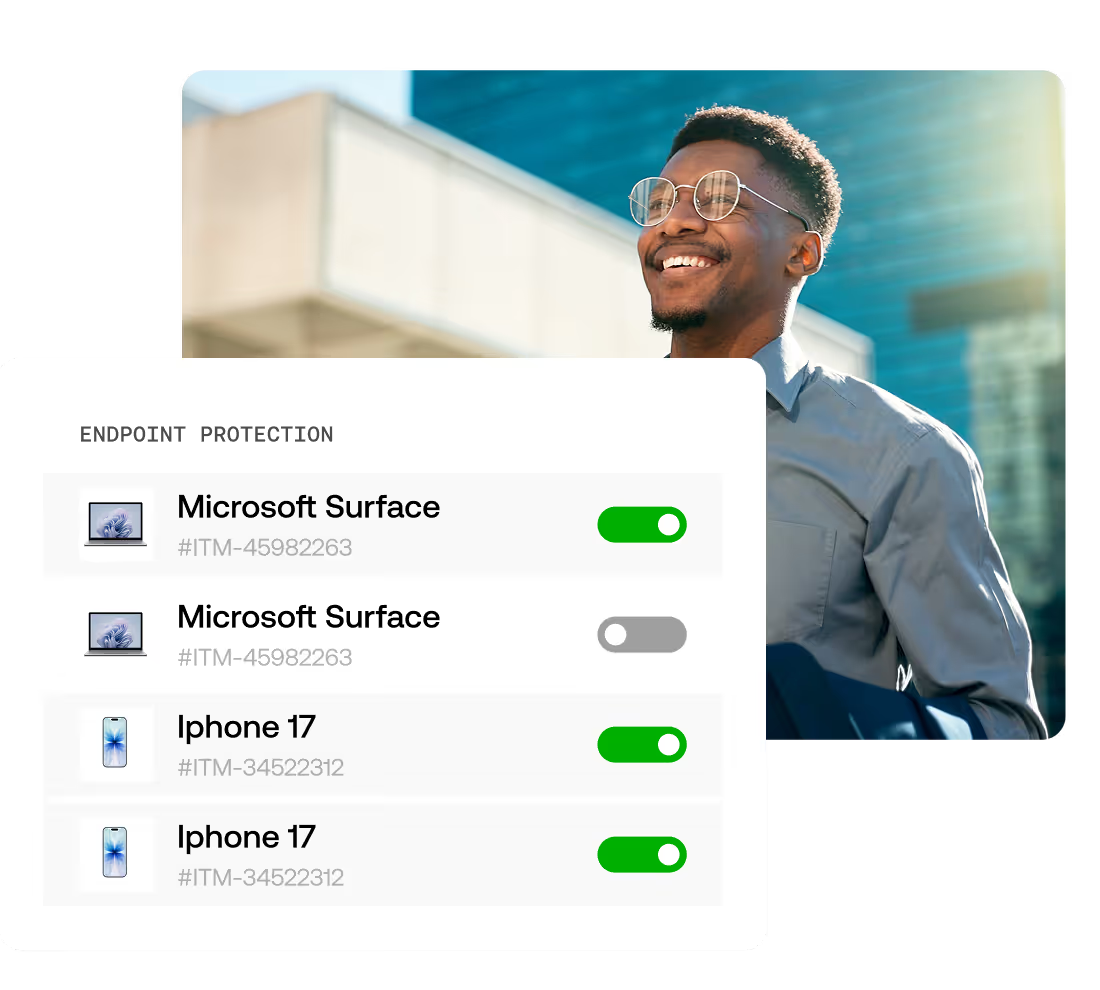
Antivirus alone does not see what is really happening on your endpoints
Modern attackers use legitimate tools that do not trigger a signature. Without behavioral detection, they remain invisible.
Fileless attacks remain invisible
Attackers exploit PowerShell and WMI. Since there is no malicious file, signature-based antivirus does not trigger an alarm.
Attacks are discovered too late
Without continuous telemetry, a compromise remains invisible for months. Attackers have plenty of time to cause damage.
No forensic context during incidents
During an incident, you don't know how it started or which systems were affected. As a result, investigation and recovery take much longer.
Detection, analysis, and response one layer deeper than antivirus
EDR is more than just technology. It requires proper management, continuous monitoring, analysis, and rapid follow-up.
Behavioral detection instead of signatures
We analyze the behavior of processes, scripts, and users. Suspicious patterns are recognized, even without known malware signatures.
Continuous telemetry from every endpoint
Process starts, network connections, and file modifications are recorded continuously. This allows an attack to be traced back to the initial suspicious process.
Process tree analysis for every alert
Our analysts see the full chain: which process started which process, and with what command line. No isolated alerts, just context.
Active response, not just detection
In the event of a confirmed threat: device isolation, process kill, and IOC sweep across your entire endpoint fleet. Immediate intervention, no waiting.
How we implement EDR on your endpoints
Controlled rollout within your existing environment, without disrupting users.
Endpoint inventory
We map out which laptops, servers, and existing tools are active. This allows us to work seamlessly alongside Microsoft Defender AV.
EDR agent rollout
The agent is rolled out in phases across laptops, servers, and workstations. It runs lightweight with no noticeable impact on performance.
Tuning of detection rules and telemetry
Detection rules are tailored to your environment. This prevents false positives and increases signal quality.
24/7 monitoring and active response
The analysts in our Security Operations Center monitor continuously. In the event of threats, device isolation, process kills, and an IOC sweep follow immediately.
Why choose managed EDR from Aumatics alongside Microsoft Defender
Microsoft Defender Antivirus is a good starting point and does not need to be disabled. However, for organizations with business-critical systems, we recommend deploying a more mature EDR solution alongside it for the following reasons:
Microsoft Defender only, no managed EDR
There is a greater risk that attacks are only discovered once systems are already infected.
Attacks are discovered (too) late
Without telemetry, you miss the moment a process exhibits suspicious behavior.
No forensic context
You don't know how an attack started or which systems have been affected.
No concrete response
Your IT team has to act ad hoc. This costs time and increases the damage.
With managed EDR by Aumatics
Better control over advanced threats and more proactive action.
24/7 Behavioral Detection
Suspicious patterns recognized instantly, including fileless attacks and suspicious PowerShell.
Process tree with every alert
Full chain visibility: which process, which command line, which connections.
Device isolation within minutes
In the event of a threat, the endpoint is immediately disconnected. Spread stopped.
Process kill and IOC sweep
Malicious processes terminated, with the same indicators searched for across all your endpoints.
Post-incident report
What happened, what actions were taken, and what has been tightened.
Built on proven technology.
We manage environments built on Palo Alto, Fortinet, WatchGuard, and other enterprise solutions. Not as standalone components, but as a coherent infrastructure. You don't have to compromise on existing investments. We ensure alignment, standardisation, and clear management processes.
Security according to demonstrably high standards
When it comes to security, you don't want to rely on loose agreements or good intentions. With our ISO 27001 certification, you know that information security is structurally organized, monitored, and improved.

Broad coverage with centralized expertise
You get a single point of contact, backed by the strength of a regional presence and specialized hubs across the country. This allows you to benefit from local engagement and shared expertise.

Trusted by IT leaders in the Netherlands
Your IT and security partner for Dutch organizations for over 25 years.
FAQ
What you should know before getting started with our managed EDR
These are the questions organizations often ask us. Do you have another question?
Can't find your question?
No problem. Feel free to let us know what questions you have!
Traditional antivirus mainly focuses on known malware. EDR looks at behaviour on endpoints and can therefore also detect new or advanced attacks. That's why many organisations combine their existing endpoint protection with EDR.
Modern EDR solutions are designed to run lightly on systems. In most environments, users notice no difference in performance. During implementation, we make sure the configuration is properly matched to your environment.
EDR generates alerts that require analysis. That's why many organisations choose to combine EDR with our Security Operations Center (SOC) or Managed Detection and Response (MDR) services. This way, your IT team only receives alerts that are genuinely relevant, while we handle most alerts on your behalf.
EDR continuously monitors endpoints and analyses suspicious activities in real time. Many threats are therefore spotted at an early stage. This helps stop attacks before they can spread further.
EDR is usually installed on laptops, workstations, and servers. This can cover Windows, macOS, and Linux systems, depending on the solution. That way, you gain visibility across virtually all endpoints within your organisation.
Suspicious activities are flagged and analysed immediately. Depending on the situation, a system can be isolated or a process stopped, for example. This limits further damage.


