Managed Detection & Response (MDR)
Our security analysts continuously monitor your endpoints, identities, and network, intervening immediately upon suspicious activity. From ransomware to MFA fatigue: we stop threats before they cause damage.
What goes wrong without managed detection & response
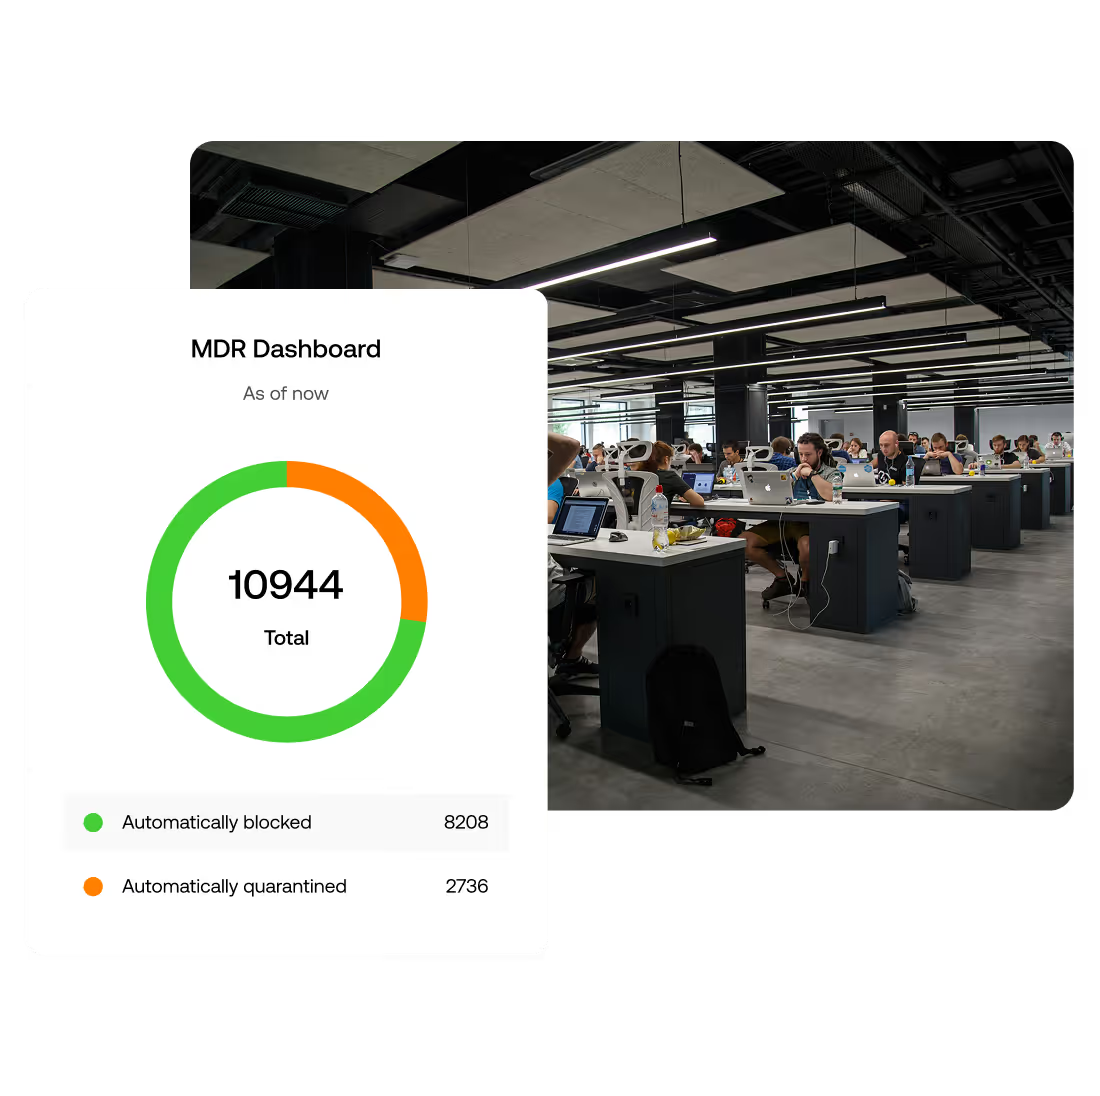
Your EDR/XDR tooling generates thousands of alerts every day. But without a team to analyze and follow up on them 24/7, threats remain undetected.
Alerts are left unaddressed
EDR platforms generate hundreds of alerts daily. Without an MDR team to analyze and follow up on every alert, critical signals are lost in the noise.
Attacks are discovered too late
From suspicious PowerShell scripts to MFA fatigue attacks: without 24/7 analysis by security specialists, these signals go unnoticed until damage is done.
Incident response takes too long
Without a defined response process, a ransomware attack can spread across your network within minutes. Every hour of delay increases the impact and recovery costs.
Why MDR with Aumatics?
Why organizations entrust their security to Aumatics.
Human layer on top of tooling
MDR is more than just an XDR/EDR platform. Our security analysts analyze every alert and take immediate action. You get a team that is ready for you 24/7, not just software that generates notifications.
Defined response process for every type of attack
From ransomware containment to stopping MFA fatigue attacks and blocking suspicious PowerShell: our analysts have a defined response process ready for every scenario.
Beyond the endpoint: identity, network, and cloud
MDR goes beyond just endpoint detection. We also monitor identity attacks, lateral movement, and suspicious network traffic. This ensures there are no blind spots in your environment.
Hybrid IT specialists
No alert fatigue for your IT team. Our analysts filter, analyze, and escalate based on fixed severity levels. Your team only receives notifications that truly require action.
How our MDR service protects your organization
MDR consists of people, processes, and tooling. This is how our analysts monitor and protect your environment 24/7:
Continuous monitoring & detection
Endpoints, identity systems, and network traffic are monitored 24/7. Suspicious activities such as suspicious PowerShell executions, unusual logins, or lateral movement are automatically detected and sent to our analysts.
Analysis & validation by analysts
Every alert is validated by a security analyst. False positives are filtered out, and real threats are classified by severity (P1 to P4). Your IT team only receives notifications that truly require action.
Immediate response & containment
In the event of a confirmed threat, our analysts intervene immediately. This includes isolating infected systems, blocking suspicious accounts, or stopping malicious processes. P1 incidents are addressed within 15 minutes.
Reporting & continuous improvement
After every incident, you will receive a report including a root cause analysis. Detection rules are refined, and your security posture improves continuously. Every attack makes you more resilient.
Full managed security across your entire IT landscape
With our MDR service, your entire environment is monitored 24/7 by security analysts. From endpoints to cloud, from identity to network traffic. We detect, analyze, and stop threats across the board.
Why choose Managed Detection & Response from Aumatics?
Leave threat mitigation to the security specialists at Aumatics and prevent unnecessary risks and incidents.
Without MDR from Aumatics
Attacks are often only discovered once systems are already infected.
Alerts without follow-up
EDR tooling generates notifications, but without analysts to review them, alerts pile up without action.
No coverage outside office hours
Ransomware strikes specifically at night and on weekends. Without 24/7 staffing, no one intervenes.
No defined response process
During an attack, your IT team has to act ad hoc. This costs time and increases the damage.
MFA fatigue and identity attacks go undetected
Modern attacks target identities, not just endpoints. Without MDR, these remain invisible.
With MDR from Aumatics
Rapid detection and immediate action on suspicious activity.
Ransomware contained within minutes
Infected systems are isolated immediately, malicious processes are terminated, and accounts are blocked.
P1 response time within 15 minutes
Security analysts initiate incident response immediately upon detecting critical threats.
MFA fatigue and suspicious PowerShell stopped
Concrete response to modern attack techniques, not just traditional malware.
24/7 staffing by security analysts
Including nights and weekends. Not just tooling, but real people analyzing and intervening.
Reporting and continuous improvement
You receive a report after every incident. Detection rules are refined so that similar attacks can be stopped more quickly in the future.
Built on proven technology.
We manage environments built on Palo Alto, Fortinet, WatchGuard, and other enterprise solutions. Not as standalone components, but as a coherent infrastructure. You don't have to compromise on existing investments. We ensure alignment, standardisation, and clear management processes.


Trusted by IT leaders in the Netherlands
Your IT and security partner for Dutch organizations for over 25 years.
Security according to demonstrably high standards
When it comes to security, you don't want to rely on loose agreements or good intentions. With our ISO 27001 certification, you know that information security is structurally organized, monitored, and improved.

Broad coverage with centralized expertise
You get a single point of contact, backed by the strength of a regional presence and specialized hubs across the country. This allows you to benefit from local engagement and shared expertise.

FAQ
What you should know before getting started with our MDR
These are the questions organizations often ask us. Do you have another question?
Can't find your question?
No problem. Feel free to let us know what questions you have!
If your IT systems are business-critical, you want to detect attacks early. Many threats go unnoticed until damage is done. MDR monitors continuously and intervenes when suspicious activity is detected.
Antivirus and Endpoint Detection and Response (EDR) generate plenty of alerts but require analysis and follow-up. MDR adds security specialists and continuous monitoring on top. That way, threats are recognised and addressed faster.
Costs depend on your IT environment and number of systems. We usually start with a short analysis of your environment. Based on that, we put together a proposal that fits your risk profile and scale.
Our security team analyses the activity immediately. When a threat is confirmed, we advise on the right actions, such as isolating a system. This way, further damage is quickly contained.
Yes. The MDR software filters and analyses alerts before they reach your IT team. You only receive alerts that genuinely require action. That way, your team stays focused on management and projects.
More about cybersecurity and MDR
Dive into MDR, SOC, and 24/7 detection and response with our practical articles.
15/10/2026
DORA Legislation: Why your organization needs to be aware of it
Discover how DORA legislation helps financial firms better protect against cyber threats and operational disruptions, and the requirements companies must meet.